Enterprise Cybersecurity, Threat Defense & Regulatory Compliance

Defend mission-critical infrastructure, achieve rigorous regulatory certifications, and eliminate attack vectors with certified cybersecurity specialists.

Protect critical enterprise networks with our comprehensive cyber security services and regulatory compliance consulting. As a top cybersecurity consulting company, we engineer Zero-Trust security architectures, conduct comprehensive penetration testing services, and enforce rigorous SOC2 & HIPAA compliance audits to safeguard digital assets against zero-day threats.

Enterprise Architecture
•
3-5 Mo MVP Velocity
•
SOC2 & ISO Ready

CYBER SECURITY & COMPLIANCE

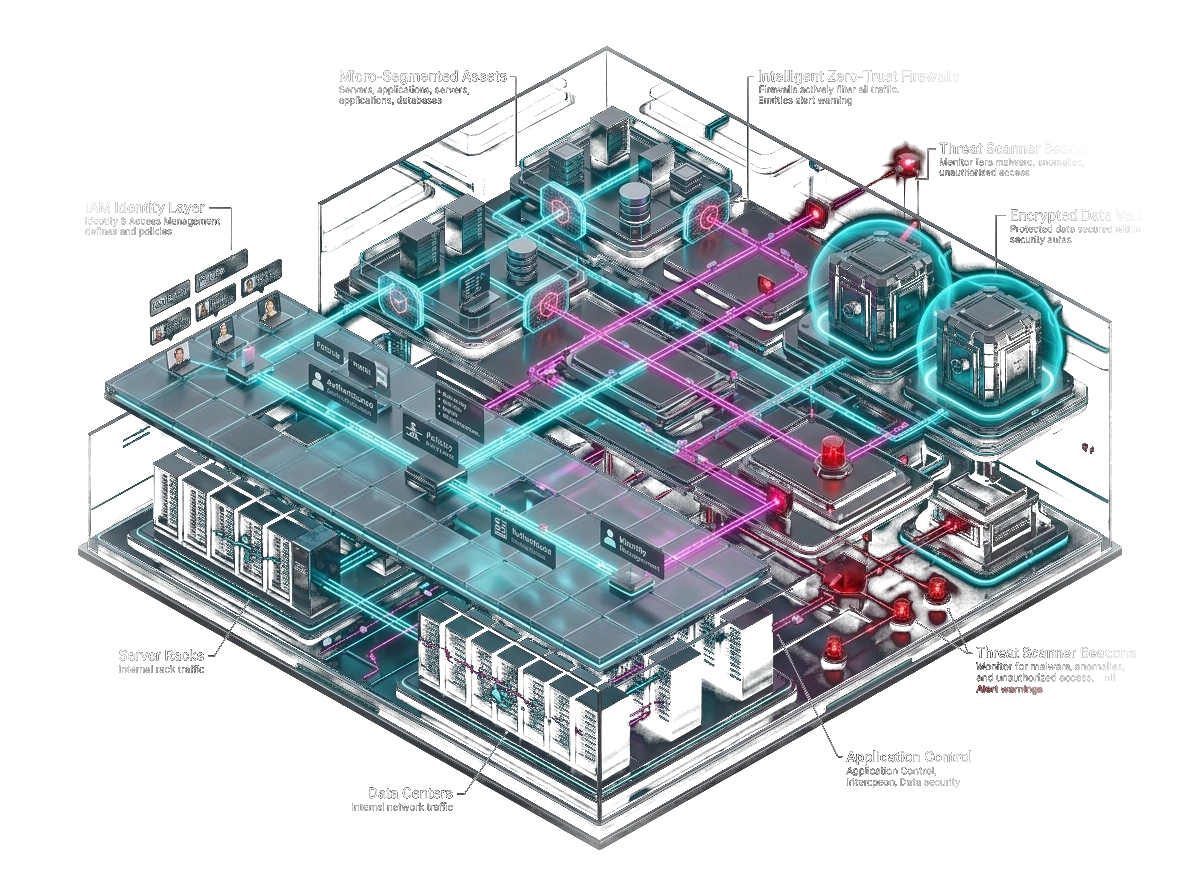
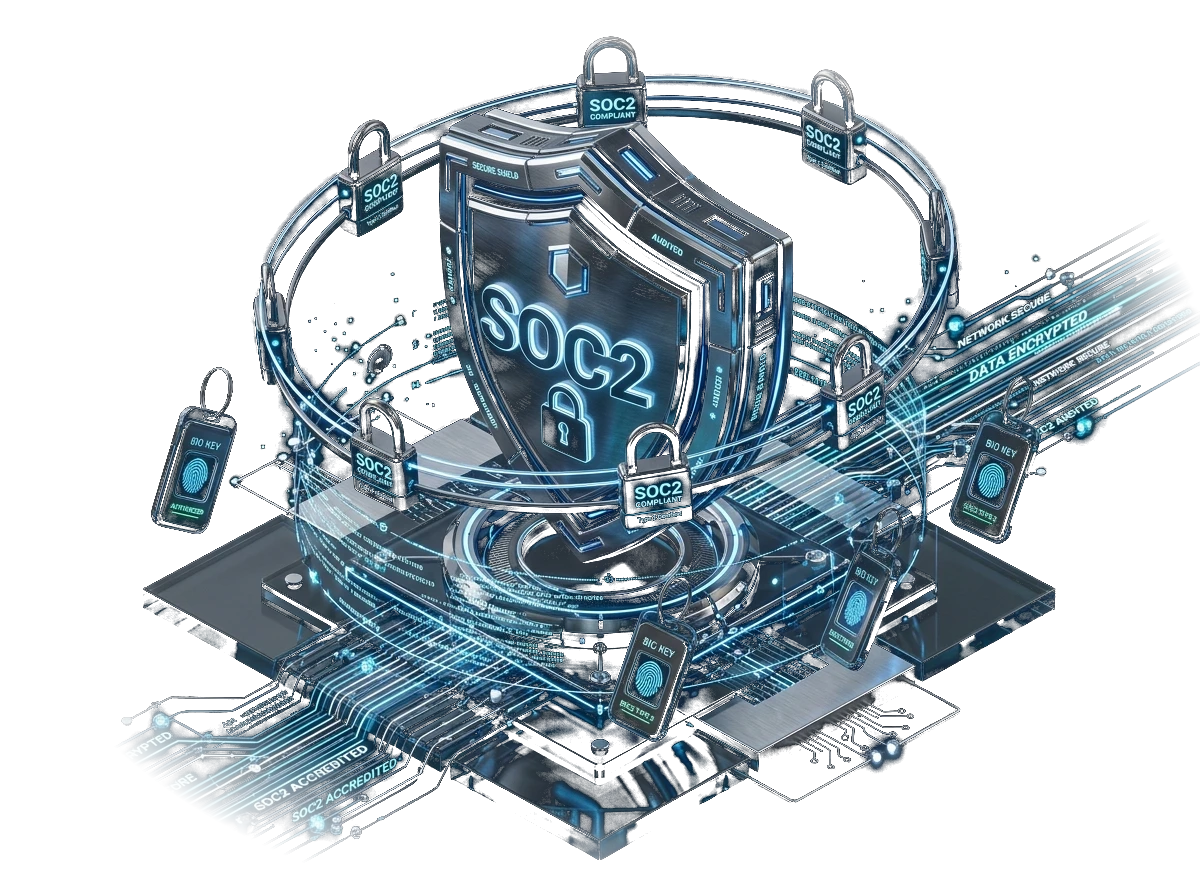
Protecting Enterprise Systems with Zero-Trust Cyber Security Shields

At Leapsofts, we engineer resilient, multi-layered enterprise defensive perimeters designed to isolate digital threats, eliminate vulnerabilities, and protect mission-critical digital assets. Modern distributed enterprises face an expanding threat surface fueled by cloud adoption, hybrid remote workforces, and sophisticated automated exploit bots. Our certified cybersecurity engineers (CISSP, CISM, CEH) implement comprehensive Zero-Trust Network Access (ZTNA), configure automated static and dynamic code vulnerability scanners (SAST/DAST) in continuous CI/CD pipelines, and deploy around-the-clock SIEM telemetry monitoring across Splunk and Datadog. Whether fortifying cloud infrastructure across AWS, Azure, and GCP or preparing for strict SOC 2 Type II, HIPAA, ISO 27001, and GDPR regulatory compliance audits, we ensure complete operational integrity and data sovereignty.

Schedule a call to talk about how we can prepare your software for the real world, or keep reading to learn more about our approach.
Protecting Enterprise Systems with  Zero-Trust Cyber Security  Shields - Leapsofts

Cyber Security Capabilities

Zero-Trust Architecture & Threat Protection
< 01 >

Zero-Trust Architecture & Threat Protection

Zero-Trust Network Access (ZTNA): Enforcing continuous authentication, least-privilege identity controls, and micro-segmented network perimeters across all hybrid cloud workloads and remote access endpoints.

Automated Threat Vector Scanning: Deploying real-time SIEM and EDR threat intelligence beacons across server clusters to identify anomalous network activity and neutralize attack vectors instantly.

Bank-Grade Data Encryption: Securing sensitive data-at-rest and data-in-transit utilizing AES-256 and TLS 1.3 envelope encryption protocols with automated HashiCorp Vault secrets rotation.

SOC2 & HIPAA Compliance Certification Audit
< 02 >

SOC2 & HIPAA Compliance Certification Audit

SOC2 Type II & ISO 27001 Preparedness: Conducting end-to-end security control audits, drafting mandatory policy documentation, and implementing automated continuous evidence collection suites.

HIPAA & GDPR Privacy Frameworks: Structuring PHI/PII data isolation barriers, access log retention policies, cryptographic hashing, and user consent registries to pass regulatory inspections.

Penetration Testing & Vulnerability Audits: Executing ethical red-team penetration tests and automated SAST/DAST code sweeps to identify and patch system zero-days before production release.

SECURITY BENEFITS

Why Prioritize Enterprise Security Now

Proactively eliminate vulnerabilities, guarantee continuous operational uptime, and secure customer trust in a hostile digital landscape.

01

Minimized Threat Attack Vector

Proactively shut down potential entry paths by scanning exposed ports, tracing irregular directory behaviors, and sanitizing database queries before exploitation.

02

Uninterrupted High-Availability Operations

Ensure your core transaction engines and customer-facing portals remain fully operational even during sustained multi-gigabit DDoS attacks.

03

Rigorous Global Regulatory Readiness

Achieve elite enterprise compliance ratings across SOC 2, HIPAA, and ISO 27001, preventing catastrophic regulatory fines and operational license suspensions.

04

Elevated User Record Security & Trust

Foster unshakeable brand loyalty by safeguarding customer identity records, payment tokens, and corporate intellectual property behind bank-grade encryption.

COMPLIMENTARY STRATEGY SESSION

Map your cybersecurity roadmap.

Whether assessing your enterprise infrastructure for an upcoming SOC 2 Type II audit, investigating a suspected vulnerability vector, or transitioning legacy networks toward a Zero-Trust security model, our certified cybersecurity specialists provide immediate technical clarity. We conduct a high-level attack surface assessment, review IAM configurations, and draft a prioritized threat remediation blueprint.
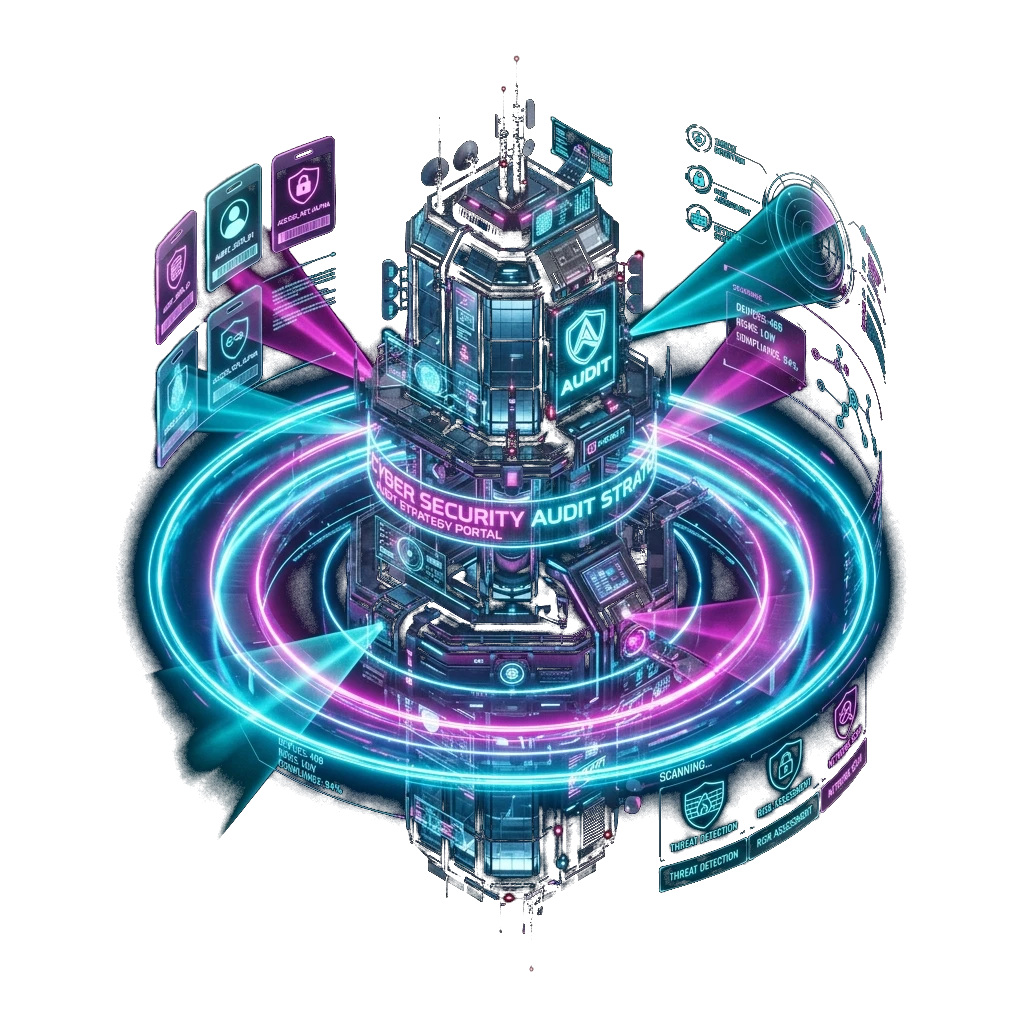
45-Min Architecture Audit
NDA & IP Protected
Actionable Tech Blueprint
✓No commitment required • Direct consultation with senior solution architects
Strategy Session Dashboard
SERVICE-SPECIFIC FEATURES

Expert Defensive Skills & Capabilities

We deliver specialized security services to support your entire organization.

Penetration Testing & Red-Teaming

Penetration Testing & Red-Teaming

Executing simulated multi-stage cyberattacks against software networks, APIs, and databases to locate authorization holes and privilege escalation vectors.

24/7 Managed Security Operations (SOC)

24/7 Managed Security Operations (SOC)

Deploying an around-the-clock Security Operations Center to discover, triage, and mitigate incoming threat vectors and suspicious network anomalies.
Multi-Cloud Infrastructure Hardening

Multi-Cloud Infrastructure Hardening

Hardening public and private cloud configurations across AWS, Azure, and GCP using automated CIS benchmarks, IAM guardrails, and VPC peering isolation.
Cryptographic Envelope & Key Management

Cryptographic Envelope & Key Management

Enforcing AES-256 data-at-rest encryption, TLS 1.3 transport security, and automated cryptographic key rotation via AWS KMS or HashiCorp Vault.

SECURITY EXCELLENCE

Our Commitment to Deliver Your Security Framework in 3-5 months

Leapsofts is an elite custom cybersecurity and risk advisory engineering partner. Combining deep threat modeling rigor, certified security engineers (CISSP, CISM, CEH), and automated DevSecOps CI/CD gates, we fortify enterprise infrastructure, remediate critical vulnerabilities, and achieve audit readiness within an accelerated 3 to 5 month delivery window.
Leapsofts Logo
SECURITY SERVICES

Threat Protection

We provide end-to-end security solutions to protect your organization from evolving digital threats, internal vulnerabilities, and compliance liabilities.

enterprise
01

Vulnerability Audits & Code Defect Scans

Conducting automated static (SAST) and dynamic (DAST) analysis scans with SonarQube, Snyk, and Trivy to discover backdoors and CVE dependency vulnerabilities.

product
02

Incident Response & Forensic Isolation

Deploying immediate incident containment protocols, isolating compromised nodes, revoking credentials, and conducting deep memory root-cause forensics.

thirdParty
03

24/7 SIEM Continuous Threat Monitoring

Orchestrating real-time telemetry scans utilizing Splunk, Datadog, or ELK setups to trace irregular database queries, lateral movements, and port scans.

legacy
04

SOC2, HIPAA, & GDPR Compliance Shield

Auditing internal configurations, user directory logs, and cloud network architectures to establish bulletproof compliance documentation and controls.

hipaa
05

Zero-Trust Identity & IAM Governance

Enforcing strict Multi-Factor Authentication (MFA), role-based access controls (RBAC), least-privilege policies, and automated credential rotation.

enterprise
06

Enterprise Network & Transport Fortification

Deploying Cloudflare Magic Transit edge protection, automated WAF rate-limiting triggers, and end-to-end TLS 1.3 encryption across all API gateways.

OUR CUSTOM CYBERSECURITY PROCESS
Phase 4SOC TELEMETRY & GOVERNANCE
Phase 3SECURITY CODING & PENTESTS
Phase 2ZERO-TRUST & ENCRYPTION
Phase 1STRATEGY & DISCOVERY
PHASE 1: THREAT LANDSCAPE DISCOVERY & AUDITING

Perimeter Auditing & Threat Profiling

We map external domain boundaries, profile user access logs, audit codebase dependencies, and establish vulnerability baselines.

  • ❯Domain Perimeter & Attack Surface Mapping
  • ❯Codebase SAST & Dependency Auditing
  • ❯Compliance Gap Analysis (SOC 2 / HIPAA)
PHASE 1
PHASE 2
PHASE 3
PHASE 4

Cyber Security & Compliance FAQ

Everything you need to know about penetration testing, SOC2/HIPAA compliance audits, Zero-Trust IAM, and SIEM monitoring.

Leapsofts delivers comprehensive enterprise cybersecurity services designed to identify vulnerabilities and defend critical infrastructure. Our core services include black-box, white-box, and gray-box penetration testing for web applications, mobile apps, and REST/GraphQL APIs. We also conduct cloud security posture management (CSPM) audits across AWS, Azure, and GCP, automated Static and Dynamic Application Security Testing (SAST/DAST) in CI/CD pipelines, Zero-Trust network architecture engineering, and 24/7 Managed Security Operations Center (SOC) threat monitoring backed by Splunk and Datadog.
We provide structured compliance readiness programs that transform complex regulatory requirements into concrete technical controls. For SOC 2 Type II and ISO 27001, our certified auditors assess your current security policies, map access control lists, configure automated evidence collection tools (such as Vanta or Drata), and implement technical controls covering change management, encryption, and business continuity. For HIPAA and GDPR, we enforce Protected Health Information (PHI) and PII data isolation, encrypted log retention, field-level tokenization, and strict data subject access request (DSAR) workflows to guarantee clean audit sign-offs.
Zero-Trust operates on the principle of "never trust, always verify." Rather than assuming internal networks are safe, Zero-Trust requires continuous identity verification, granular authorization, and strict micro-segmentation for every user and microservice. We implement Zero-Trust Network Access (ZTNA) by deploying centralized identity providers (Okta, Azure AD) with adaptive Multi-Factor Authentication (MFA), enforcing least-privilege Role-Based Access Control (RBAC), isolating sensitive database subnets within private VPCs, and requiring Mutual TLS (mTLS) for all inter-service communications.
We architect centralized Security Information and Event Management (SIEM) systems using industry-leading platforms including Splunk, Datadog Cloud SIEM, Elastic Security (ELK Stack), and AWS GuardDuty. We configure automated log shippers to collect telemetry from firewalls, Kubernetes ingress controllers, API gateways, and database access logs. Our engineers author custom behavioral correlation rules and anomaly detection algorithms that detect lateral movements, brute-force attempts, and unauthorized data downloads, immediately alerting on-call security engineers via integrated PagerDuty workflows.
Our DevSecOps approach shifts security to the earliest stages of software development ("shift-left"). We integrate automated security checks directly into GitHub Actions, GitLab CI, and Bitbucket runners. Every pull request triggers automated SAST scans using SonarQube, container and open-source dependency vulnerability scans using Trivy and Snyk, and hardcoded secret detection using GitGuardian. Builds containing critical or high Common Vulnerabilities and Exposures (CVEs) are automatically blocked from staging and production promotion until remediated.
We recommend a tiered, continuous vulnerability management cadence. Automated static code analysis and dependency CVE checks should run continuously on every code commit. Dynamic application scans (DAST) and external infrastructure port scans should occur weekly or bi-weekly. Comprehensive manual penetration tests conducted by certified ethical hackers (OSCP, CEH) should be performed at least annually for SOC 2 compliance, and whenever major architectural updates, third-party integrations, or product releases occur.
We maintain an aggressive, structured Incident Response Plan (IRP) with sub-15-minute response SLAs for critical security events. The response protocol executes in four stages: immediate containment (isolating infected virtual machines, revoking active session tokens, and blacklisting compromised IP ranges); root-cause forensic investigation (analyzing memory dumps, system logs, and network traffic); rapid remediation (patching exploit vectors, rotating compromised credentials, and applying security hotfixes); and transparent post-incident reporting with regulatory notification guidance.
We apply the Center for Internet Security (CIS) Cloud Benchmarks across AWS, Azure, and GCP. Our cloud hardening includes removing default VPCs, enforcing strict Security Group and Network Access Control List (NACL) egress filtering, enabling cloud audit trails (AWS CloudTrail, Azure Activity Log), enforcing multi-region database backups with immutable object locks, and implementing AWS KMS or Azure Key Vault for envelope encryption of data-at-rest. Furthermore, we deploy Cloud Security Posture Management (CSPM) tools to automatically detect and remediate configuration drift.
A comprehensive enterprise cybersecurity engagement spans 3 to 5 months, divided into focused two-week agile sprints. The first 2 to 3 weeks encompass attack surface discovery, code scanning, and external penetration testing, concluding with a detailed risk remediation matrix. Sprints 3 through 6 focus on Zero-Trust IAM deployment, network micro-segmentation, and DevSecOps pipeline automation. Sprints 7 through 9 execute SIEM integration, incident response playbooks, and compliance evidence documentation, followed by 30 days of hypercare monitoring and final audit validation.
GLOBAL ALLIANCES & CLIENT ECOSYSTEM

Trusted by pioneering startups & industry leaders.

Collaborating with certified cloud platforms and global enterprises to engineer mission-critical digital products.
Afirme
Dewford
digicars
techadvancer
aa-logo
hpe
truper
joget
osorio
cmolds
ipmd-logo
harris-paints
JBreeden
knife
newDark
Instrat

Proven technical excellence, validated by leaders.

Discover how our agile engineering pods accelerate delivery, eliminate latency bottlenecks, and scale digital products for global enterprises.

Verified Client

"The overall structure and organization of their development team is incredibly impressive."

The way they layer managers and team leaders to ensure quality and efficiency results in incredible work. It is difficult to find development firms that can match the quality of Fortune-500 standards, but Leapsofts executes at the highest level.

J
Jake ZaharaPresident, Global Guru
Verified Client

"They delivered a robust platform that exceeded our scalability requirements by 200%."

Their technical expertise in distributed systems is unmatched. We were facing severe latency issues with our previous provider, but the Leapsofts team architected a solution that handled our peak loads effortlessly.

S
Sarah JenkinsCTO, FinTech Sol
Verified Client

"Exceptional attention to detail and a true partnership approach to problem-solving."

Unlike other vendors who just execute tickets, Leapsofts challenges our assumptions and helps us build better products. Their input on the architecture and UX overhaul was instrumental in boosting our retention.

M
Michael ChangProduct Director, Nexus

Succeed faster with Leapsofts

If you submit a request today, your MVP will be ready as early as January 12, 2027

+1

This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply.