Enterprise Quality Assurance & Software Testing Services
Prevent production failures before they happen. Comprehensive QA engineering integrated directly into your CI/CD pipeline.
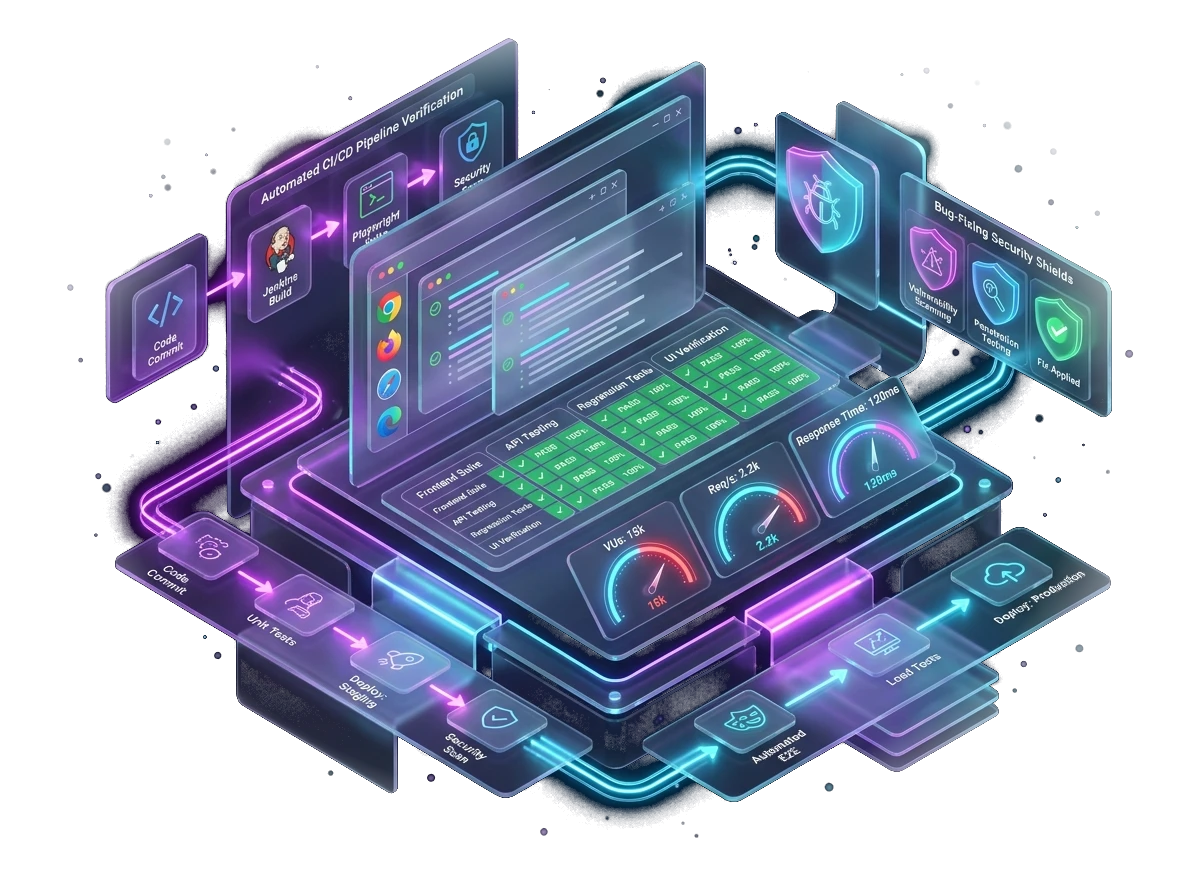
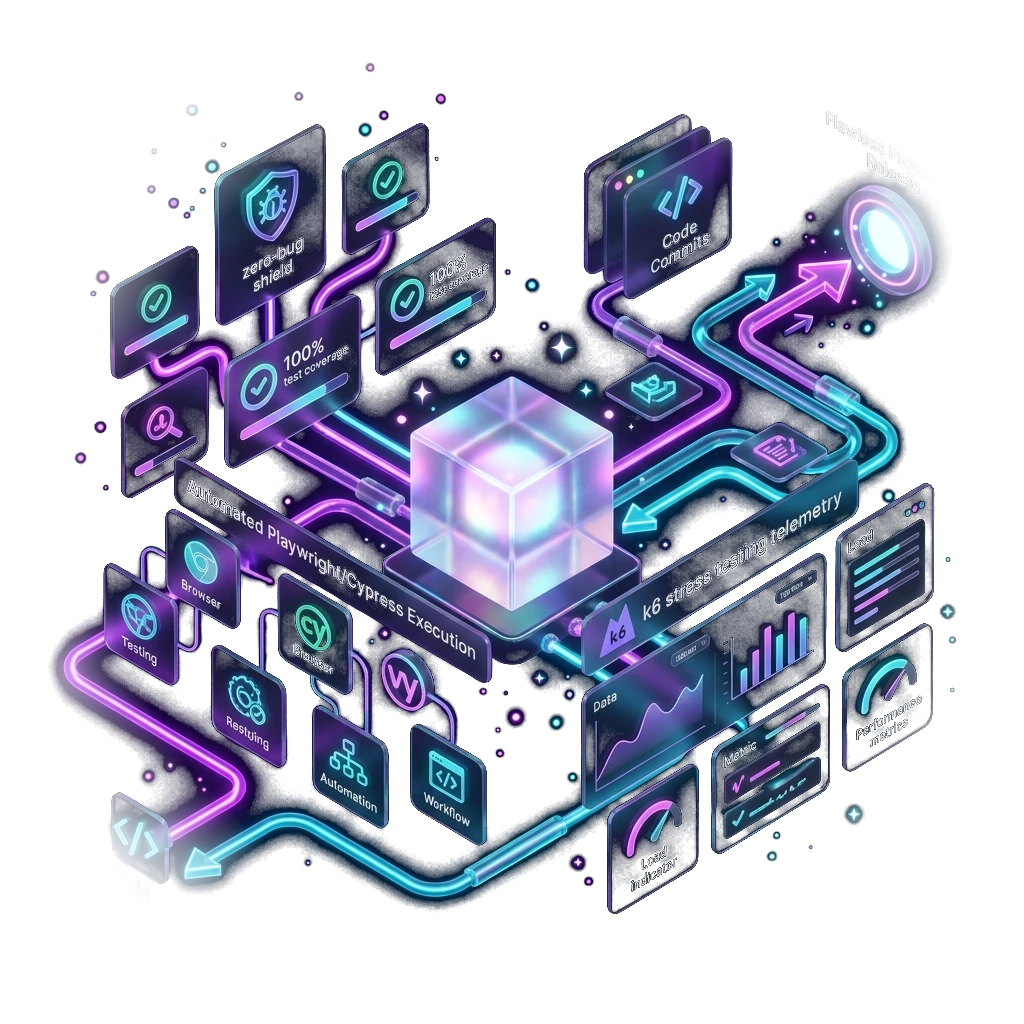
We deliver full-spectrum quality assurance services and software testing solutions engineered to eliminate functional regressions, stress-test database limits, and secure critical application networks. As a premier software testing company, Leapsofts embeds automated QA testing frameworks — Playwright, Cypress, Jest, k6 — directly into your CI/CD pipelines, ensuring every code commit is validated against functional, performance, and security criteria before reaching production.
QUALITY ASSURANCE & TEST ENGINEERING
Continuous Software Validation & Security Assurance
Schedule a call to talk about how we can prepare your software for the real world, or keep reading to learn more about our approach.
Why Enterprise QA Engineering Delivers ROI
Production bugs cost 100x more to fix than development-phase defects. Professional QA engineering eliminates that risk, accelerates release cadence, and protects brand reputation.
Early-Stage Defect Cost Elimination
Catching and resolving bugs during the development sprint costs 10–100x less than post-release hotfixes. Our shift-left QA methodology embeds quality gates from Day 1, reducing total debugging overhead and dramatically accelerating release timelines.
Defect-Free User Experience Across All Devices
Automated cross-browser, cross-device, and cross-resolution testing ensures your application renders and performs identically on Chrome, Firefox, Safari, Edge, iOS, and Android — eliminating experience inconsistencies that drive user churn.
Zero-Trust Security & Compliance Assurance
Systematic OWASP Top 10 vulnerability scanning, OAuth2 token validation, TLS certificate checks, and SOC2/HIPAA compliance audits protect your platform and customer data from security threats before they reach production.
Accelerated Release Velocity Without Risk
CI/CD-integrated regression shields run comprehensive test suites automatically on every commit, blocking defective code at the pipeline level. Teams release 3–5x faster knowing every build has been validated before it reaches staging or production.
Map your testing roadmap.
Our senior QA architects will audit your current testing coverage, identify your top 5 regression risk areas, and deliver a zero-disruption automation roadmap — completely free. No lock-in, no obligation. Get immediate clarity on the fastest path to bug-free, CI/CD-integrated quality engineering.
Core QA Engineering Capability Pillars
We offer specialized testing services tailored to your project requirements, ensuring robust performance and security.

Test Automation Frameworks
Building Playwright, Cypress, and Jest automation architectures with page-object models, CI/CD integration, and Allure reporting for comprehensive regression coverage on every commit.

Manual & Exploratory Testing
Rigorous human-led edge case analysis, destructive scenario testing, visual layout verification, and usability heuristic evaluations that automated scripts cannot replicate.
Performance & Load Testing
Scripting k6 and JMeter load simulations to measure API latency, server memory limits, and database connection pool behavior under thousands of concurrent virtual user sessions.
Security & Compliance Auditing
OWASP Top 10 penetration testing, OAuth2/JWT token validation, TLS certificate checks, and SOC2/HIPAA compliance verification integrated into pre-release security sign-off workflows.
Deploy Bug-Free Software in 3–5 Months
Leapsofts is an elite QA engineering partner. By embedding dedicated QA pods into your active development sprints, integrating automated test gates into your CI/CD pipelines, and executing systematic security audits before each release, we ensure every product launch meets the highest standards of functional quality, performance, and security compliance.
Software Testing Services We Deliver
From automated regression suites to security penetration testing, our QA engineering practice covers every dimension of software quality — integrated directly into your development workflow with zero disruption.

Automated Functional & Regression Testing
We build comprehensive automated test suites using Playwright and Cypress (frontend E2E), Jest and Vitest (unit/component), and Selenium WebDriver (legacy browser support). Test suites are integrated into GitHub Actions or GitLab CI pipelines and execute automatically on every pull request — blocking regressions before they reach the main branch.
Performance & High-Concurrency Load Testing
Using k6 and Apache JMeter, we script distributed load simulations that replicate thousands of concurrent virtual user sessions against your production-equivalent environment. We measure Largest Contentful Paint (LCP), Time to First Byte (TTFB), API P95/P99 response latency, server CPU saturation, and database connection pool exhaustion under sustained and spike traffic scenarios.

Unit & Component Test Suite Development
Our engineers write modular, isolated unit tests with Jest, Vitest, or JUnit for every business logic function, React component, API controller, and database query handler. We target minimum 80% code coverage with meaningful assertions — not superficial coverage — verified through Istanbul/NYC instrumentation integrated into your SonarQube quality gate.
API Integration & Contract Testing
We validate RESTful and GraphQL API contracts using Postman collections, Newman CLI automation, and Pact contract testing frameworks. Every API endpoint is verified for correct HTTP status codes, response schema validation, error handling, rate limiting behavior, and authentication boundary enforcement — across both mock and production-integrated environments.

End-to-End Browser Automation & Visual Testing
Complex multi-step user journeys — registration flows, checkout sequences, dashboard interactions, form submissions — are automated using Playwright with page-object model architecture. Visual regression tests using Percy or Chromatic capture pixel-level UI changes across Chrome, Firefox, Safari, and mobile viewports, alerting on any unexpected layout or styling regressions.
User Acceptance Testing (UAT) Management
We formulate structured UAT test plans with acceptance criteria mapped directly from business requirements and user stories. Staged UAT environments are provisioned with production-mirrored data, and we manage the full test execution cycle — test case design, tester onboarding, defect tracking in Jira/Linear, and formal sign-off documentation — before any release approval.
Continuous Regression Shielding in CI/CD
We configure automated regression shields as required GitHub Actions status checks, blocking pull request merges if any regression test fails. Test results are surfaced in Allure or Playwright HTML reports with screenshot evidence on failure, enabling engineers to identify and fix root causes in minutes rather than discovering bugs in production hours after deployment.
Security Penetration Testing & OWASP Audits
Our security QA engineers conduct systematic penetration tests targeting OWASP Top 10 vulnerabilities: SQL injection, XSS, CSRF, IDOR, broken authentication, insecure deserialization, and misconfigured CORS policies. We validate OAuth2/OpenID Connect token flows, evaluate JWT signature verification, and perform TLS certificate chain validation to confirm SOC2 and HIPAA compliance posture.
Accessibility & WCAG 2.1 Compliance Audits
We evaluate every UI component and user flow against WCAG 2.1 Level AA standards using automated axe-core scanning integrated with Playwright, complemented by manual screen reader testing with NVDA and VoiceOver. Audit reports include exact WCAG criterion violations, affected HTML elements, ARIA implementation recommendations, and keyboard navigation gap analysis.
Static Code Analysis & Quality Gate Enforcement
We configure SonarQube or SonarCloud quality gates that block deployments if code coverage drops below threshold, cyclomatic complexity exceeds limits, or new security hotspots are detected. ESLint, TypeScript strict mode, and Prettier are enforced as pre-commit Git hooks via Husky, eliminating code style issues and potential runtime errors before they enter the codebase.
OUR SOFTWARE QUALITY ASSURANCE PROCESS
 RELEASE SHIELDSEXECUTION & AUDITFRAMEWORK SETUP
 TEST STRATEGY
Test Mapping & Environment Architecture
Before writing a single test, we analyze your requirements, user stories, and architecture to build a precision QA strategy that eliminates guesswork and maximizes coverage efficiency.
- ❯Acceptance Criteria & Test Scope Definition
- ❯Test Automation Strategy & Tool Selection
- ❯Staging Environment Configuration & Data Seeding
Quality Assurance & Software Testing FAQ
Everything you need to know about automated testing, Playwright/Cypress frameworks, load testing, and continuous regression shielding.
Explore Related Engineering Capabilities
Custom Software Development
Engineer scalable web and mobile software tailored for enterprise workflows.
DevOps Services & CI/CD
Integrate automated testing and security scans into your continuous delivery pipelines.
Cyber Security & Compliance
Conduct thorough penetration audits and zero-trust vulnerability assessments.
Trusted by pioneering startups & industry leaders.
Collaborating with certified cloud platforms and global enterprises to engineer mission-critical digital products.


Proven technical excellence, validated by leaders.
Discover how our agile engineering pods accelerate delivery, eliminate latency bottlenecks, and scale digital products for global enterprises.
Succeed faster with Leapsofts
If you submit a request today, your MVP will be ready as early as January 12, 2027